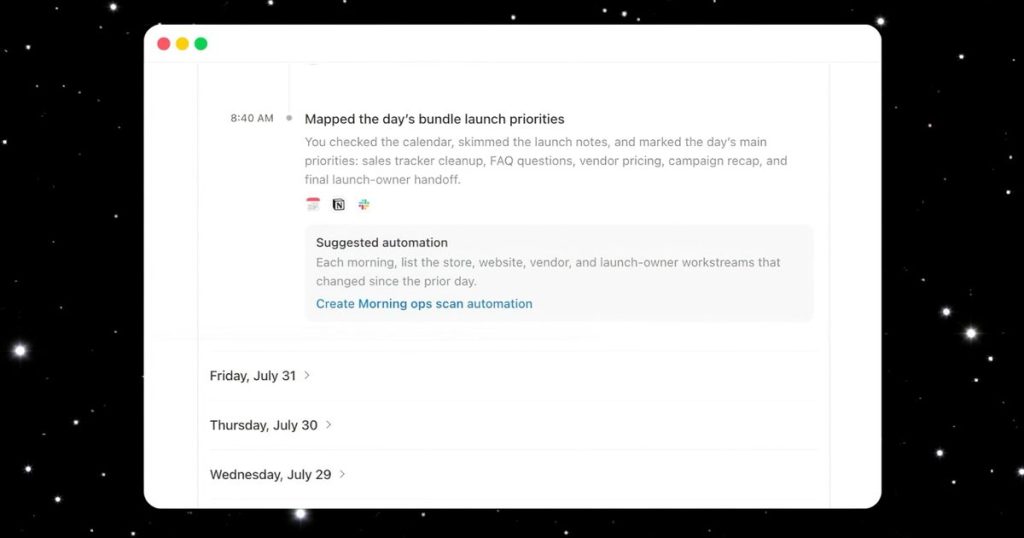
OpenAI recently introduced a Computer History feature for its macOS ChatGPT client, designed to help the desktop application track user activity across various apps and desktop workflows. While this functionality aims to make AI interactions more context-aware, a major security flaw lies hidden inside its local storage architecture.
This analysis examines the security risks of OpenAI’s Computer History feature on macOS, which logs user interactions as unencrypted plain-text files. It outlines how local malware and prompt-injection attacks can exploit these unencrypted logs, while detailing the available privacy controls for Mac users evaluating whether to enable this opt-in tool.
Unencrypted Markdown Files Create Local Vulnerabilities
Unlike traditional screen-recording tools, ChatGPT’s Computer History does not record video, capture audio, or take direct desktop screenshots. Instead, it monitors lightweight interaction events, including app switching, typing, mouse clicks, and active document usage. The feature temporarily keeps raw interaction data for 48 hours before translating these events into persistent local memories.
The main security concern stems from how OpenAI stores these local memories. According to official OpenAI documentation, these activity logs are saved as plain-text Markdown files without any encryption layer. Because these files sit unprotected on the local drive, any other application or background process running under the same macOS user account can read, copy, or parse their contents.
Security Profile of ChatGPT Computer History
| Feature Aspect | Implementation Details | Security & Privacy Impact |
|---|---|---|
| Storage Format | Plain-text Markdown (.md) stored locally on macOS | High risk due to lack of local encryption |
| Retention Period | Raw event files purged after 48 hours; derived logs persist | Moderate risk of long-term data accumulation |
| Monitored Activity | App switches, typing events, clicks, document titles, web visits | High sensitivity regarding personal workflow habits |
| System Access Level | Accessible by any process executing under the same user profile | High vulnerability to existing local malware |
| User Mitigations | Opt-in toggle, exclusion lists for apps/sites, manual deletion | Effective for limiting scope, but does not encrypt saved logs |
How Local Malware and Prompt Injection Threaten Activity Logs
The absence of local file encryption means the primary threat does not require a breach of OpenAI’s cloud servers. Instead, the real risk comes from malicious software already present on a user’s Mac. If adware, spyware, or an unauthorized script gains execution rights under your user account, it can quietly locate and harvest these Markdown files to siphon sensitive context about your work habits, visited URLs, and document names.
Beyond traditional malware, broad contextual history introduces a secondary vector: prompt injection. If an attacker places hidden malicious instructions inside a website or document that you view, those instructions could theoretically be saved into your computer history. When ChatGPT reads its own historical memory later, those injected prompts could manipulate the AI’s future responses or decisions.
Evaluating Privacy Controls Before Enabling the Feature
To OpenAI’s credit, Computer History is not enabled by default. Users must actively opt in before the desktop application begins tracking system interactions. Furthermore, the software provides essential control settings that allow users to manage their exposure:
- App Exclusions: Users can define specific applications that ChatGPT must completely ignore.
- Website Exclusions: Browsing activity on designated domains can be omitted from history logs.
- Manual Log Deletion: Entries can be cleared manually at any time to remove unwanted contextual data.
While these controls help limit what the assistant remembers, they do not resolve the core storage issue. Every log entry you allow ChatGPT to keep remains accessible in plain text. Mac users must weigh the convenience of enhanced AI memory against the security tradeoffs of storing detailed activity logs unencrypted on their hard drives.
Frequently Asked Questions
Frequently Asked Questions
Is ChatGPT’s Computer History turned on by default on macOS?
No, the Computer History feature is strictly opt-in. Mac users must manually activate the feature within the desktop client’s settings before any interaction tracking or local logging takes place.
Does ChatGPT record my screen, video, or microphone audio?
No, Computer History does not record video feeds, capture audio, or take continuous screenshots. It strictly logs system interaction metadata, such as open application names, website titles, typing activity, and document interactions.
How can I protect my personal data if I choose to use Computer History?
You can minimize privacy risks by adding sensitive work applications and private websites to the feature’s exclusion list, periodically clearing stored memory logs, and ensuring your Mac runs reliable security software to prevent unauthorized local file access.